Identity Threat Detection and Response (ITDR): Securing the New Perimeter
With the adoption of cloud architectures and remote work, traditional network perimeters have been replaced by the Identity Control Plane. Adversaries rarely “break in” using exploit payloads; they “log in” using compromised credentials, stolen session tokens, or misconfigured OAuth applications.
Identity Threat Detection and Response (ITDR) provides specialized monitoring and threat hunting across identity providers (IdPs) like Active Directory, Microsoft Entra ID, and Okta.
Plaintext
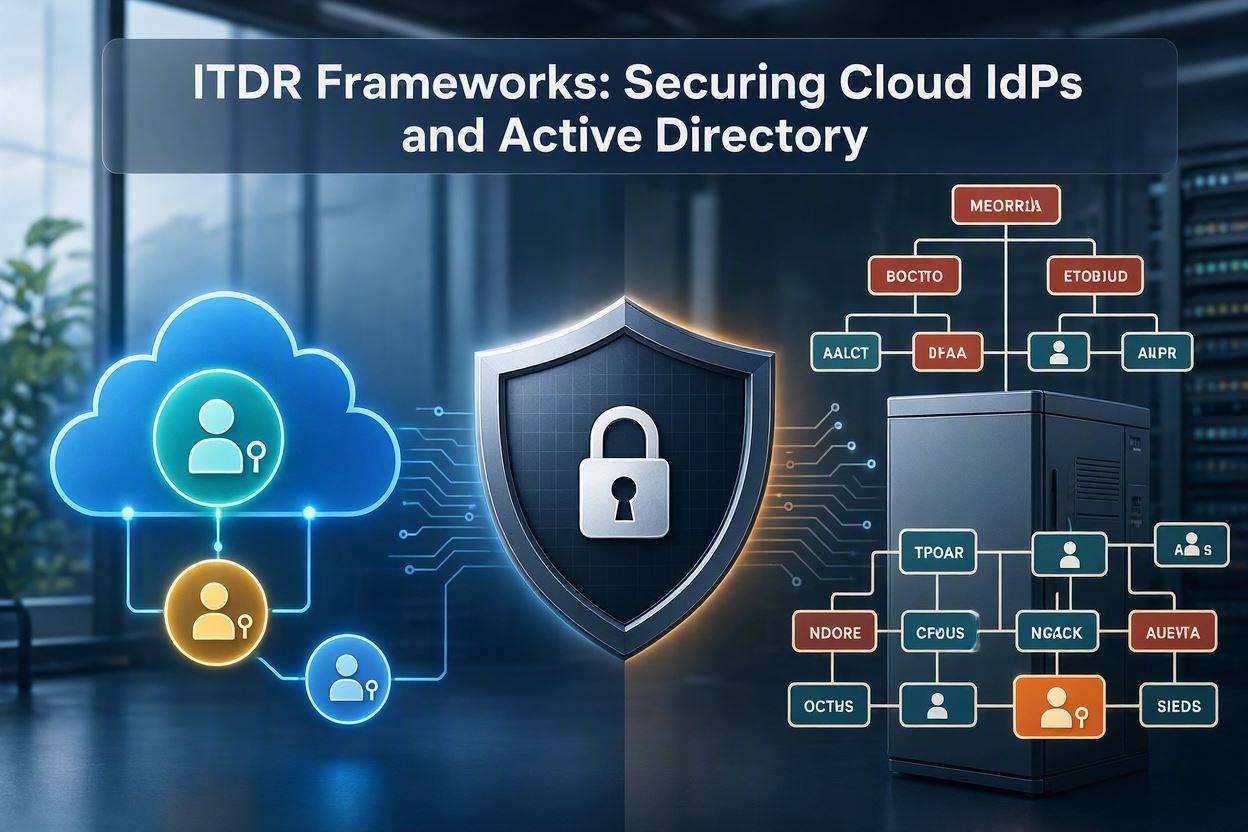
[ Stolen Refresh Token ] ──> [ IdP Authentication Attempt ] ──> [ ITDR Anomaly Engine ] ──> [ Token Revocation API ]
ITDR vs. EDR: Bridging the Visibility Gap
Endpoint Detection and Response (EDR) tracks system processes, but lacks visibility into identity provider telemetry:
| Attack Technique | EDR Monitoring Capability | ITDR Monitoring Capability |
| Pass-the-Hash / Kerberoasting | Moderate (Local Memory Context) | High (Direct DC Ticket Log Analysis) |
| OAuth App Consent Grant Exploitation | Unmonitored | High (Scopes & Permissions Audit) |
| Session Cookie Hijacking | Low (Post-Exploitation Endpoint) | High (Session Telemetry & IP Anomalies) |
| Active Directory DCSync Attack | Unmonitored (Network/RPC Level) | High (Monitors Directory Replication Requests) |
Core Capabilities of an ITDR Architecture
-
Identity Posture Management: Continuously audits Active Directory and Cloud IdPs for misconfigurations, such as stale admin accounts, weak delegation settings, or unencrypted credential stores.
-
Behavioral Anomaly Detection: Flags impossible travel anomalies, concurrent logins across distant geographic locations, and unusual administrative privilege grants.
-
Automated Incident Response: Triggers API workflows to invalidate active session tokens, force step-up authentication, or disable compromised accounts instantly upon detection.
#IdentitySecurity #ZeroTrust #ITDR #ActiveDirectory #BettyCoder